HTTP Terminator: AI Unveils New Request Smuggling Vectors
Introduction
The landscape of web application security is shifting beneath our feet. For years, HTTP request smuggling—often dubbed "desync" attacks—has remained a notoriously difficult class of vulnerability to automate. These flaws rely on subtle discrepancies in how front-end proxies and back-end servers parse the same HTTP request chain, requiring a depth of protocol understanding that traditional fuzzers simply cannot replicate. That paradigm changed recently when PortSwigger Research Director James Kettle introduced HTTP Terminator, an AI-powered, open-source utility that doesn't just fuzz endpoints—it reasons about them.
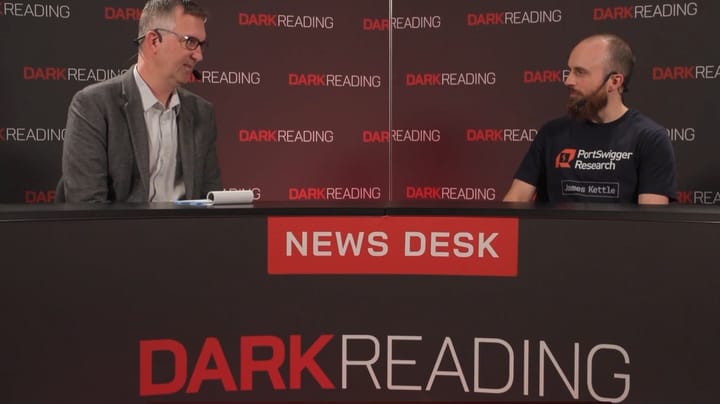
In a conversation with the Dark Reading News Desk, Kettle detailed how integrating Large Language Models (LLMs) into the vulnerability research loop has yielded previously unknown smuggling variants. This isn't just an incremental improvement in scanning technology; it represents a fundamental evolution in offensive security tooling, moving from brute-force permutation to intelligent protocol manipulation.
The Blind Spot of Traditional Scanning
To appreciate the leap HTTP Terminator represents, one must understand why request smuggling has historically evaded automated detection. Standard Dynamic Application Security Testing (DAST) scanners operate on a "send payload, check response" logic. They excel at finding reflective XSS or SQL injection because the cause-and-effect is immediate and visible in the HTTP response body.
Desync attacks, however, are stateful and blind. A successful smuggling attempt poisons the connection state between a front-end load balancer (like Nginx, HAProxy, or AWS ALB) and a back-end server. The malicious request might be perfectly valid to the front end but interpreted as two distinct requests by the back end—or vice versa. The result? The "smuggled" request prefixes the next legitimate user's request, hijacking their session or poisoning a cache. Because the attacker often sees only a generic 200 OK or a 404 for their own probe, standard scanners mark the endpoint as "not vulnerable" and move on.
Manual testing by experts like Kettle has always been the gold standard here, relying on deep knowledge of RFC 7230/9110 parsing edge cases—transfer-encoding vs. content-length conflicts, header folding, whitespace sensitivity, and the obscure handling of chunked encoding terminators. HTTP Terminator aims to bottle that expertise.
How HTTP Terminator Thinks Differently
HTTP Terminator doesn't rely on a static dictionary of known smuggling prefixes (like the classic Transfer-Encoding: chunked vs Content-Length clashes). Instead, it employs an LLM-driven mutation engine that treats the HTTP protocol as a language to be spoken fluently, rather than a format to be fuzzed randomly.
- Semantic Mutation: The AI understands the semantic intent of headers. It knows that
Content-Lengthimplies a body length, whileTransfer-Encoding: chunkedimplies a streaming format. It generates mutations that specifically target the disagreement between these semantics across different server implementations. - Context-Aware Payload Construction: Rather than blindly injecting
\rsequences, the model constructs requests that are syntactically valid for one parser but structurally ambiguous for another. It effectively performs "differential parsing" in silico before sending a single packet. - Feedback Loop Analysis: The tool analyzes timing differentials, connection resets, and subtle header reflections (like
ViaorX-Forwarded-Foranomalies) to infer backend state corruption—effectively "seeing" the blind spot.
This approach has already borne fruit. Kettle revealed that the tool identified novel desync vectors involving obscure header interactions and chunked encoding edge cases that were absent from public research repositories. These aren't just variations of CL.TE or TE.CL; they represent entirely new parsing differentials.
Implications for the Modern Attack Surface
The discovery of these novel vectors via AI has immediate, tangible consequences for defenders. Modern architectures—microservices behind API Gateways, Service Meshes (Istio/Linkerd), Serverless functions (AWS Lambda, Cloudflare Workers), and Edge Compute platforms—introduce layers of HTTP parsers that have never been stress-tested against each other in this manner.
Every layer that terminates and re-originates HTTP traffic (a "hop") is a potential desync boundary. HTTP Terminator's ability to rapidly prototype parser differentials means that the window between a new proxy version release and the discovery of a parsing quirk in that version has drastically shrunk. Organizations can no longer assume their WAF or API Gateway "normalizes" traffic sufficiently; the normalization logic itself is now the attack surface.
Grivyonx Expert Analysis
The release of HTTP Terminator marks a pivotal moment: the commoditization of logic-based vulnerability discovery. For a decade, the industry has automated "pattern matching" vulnerabilities (signatures). We are now entering the era of "reasoning" vulnerabilities. This tool proves that LLMs can model the state machines of disparate HTTP parsers and predict where they diverge.
For security teams, the takeaway is urgent: Regression testing for parsing differentials must become continuous. Every time you upgrade Nginx, Envoy, or your Cloud Provider's Load Balancer, the parsing contract changes. At Grivyonx Cloud, we are integrating similar differential analysis engines into our continuous exposure management platform. We treat HTTP parsers as distinct "dialects" and continuously verify that the dialect spoken by your Edge matches the dialect understood by your Origin. If you aren't fuzzing the *boundary* between your infrastructure layers with semantic awareness, you are blind to the exact class of flaws HTTP Terminator excels at finding.
Conclusion
James Kettle's HTTP Terminator is more than a new tool for the bug bounty toolkit; it is a proof-of-concept for the future of vulnerability research. By bridging the gap between syntactic fuzzing and semantic protocol understanding, it forces the industry to acknowledge that the most dangerous bugs are no longer simple syntax errors—they are architectural mismatches exploited by artificial intelligence. As the web stack grows more complex with every proxy, sidecar, and edge function inserted into the request path, the attack surface for desynchronization expands exponentially. Defenders must adopt tooling that thinks like the protocol, not just tooling that throws payloads at it. Grivyonx Cloud’s AI-driven automation platform is built precisely for this new reality—continuously mapping, testing, and securing the invisible seams between your infrastructure layers before attackers find them.
- #HTTP Request Smuggling
- #AI Security Tools
- #PortSwigger
- #Web Vulnerabilities
- #Cybersecurity Research
- #Desync Attacks
- #Burp Suite
- #Application Security