The Lazarus-Medusa Nexus: Analyzing the Surge in Ransomware Attacks on Healthcare
Targeting the Healing Hand
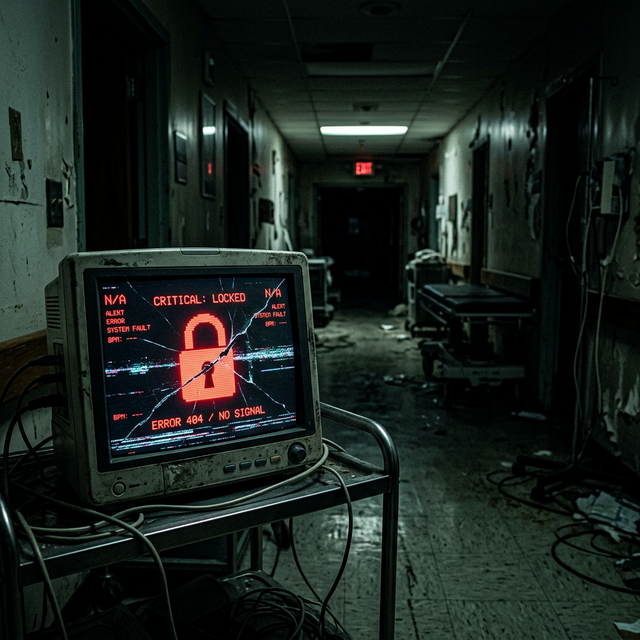
The Lazarus Group, a nation-state actor known for high-stakes financial theft, has officially partnered with the Medusa Ransomware syndicate to target the global healthcare sector. This partnership combines the surgical infiltration skills of a state-sponsored team with the brutal operational efficiency of a ransomware gang. For hospitals and medical research facilities, this represents a "Code Red" threat level.
When patient data is locked, it's not just a business loss—it's a threat to human life.
The Evolution of the Medusa Attack
The attack typically begins with Credential Stuffing targeting the VPNs of remote medical staff. Once the attackers are inside the hospital’s internal network, they use the Lazarus Group's custom "Living off the Land" techniques to move silently towards the EMR (Electronic Medical Record) databases.
Double Extortion Tactics
The Medusa gang doesn't just encrypt the data; they steal it first. They threaten to release sensitive patient histories, surgery schedules, and psychiatric records on their "shame site" unless a massive ransom is paid. The pressure is both financial and ethical.
Active Sabotage of Backups
The Lazarus-Medusa team spends days identifying and poisoning the organization's backup servers before triggering the encryption. They ensure that "restoring from backup" is impossible, leaving the organization with no choice but to negotiate.
Hardening the Healthcare Infrastructure
Healthcare security requires a unique balance of accessibility and protection. Here is the Grivyonx strategy for medical data resilience:
- Micro-Segmentation of EMRs: Your patient database should be isolated from the rest of the hospital network. Even if a nurse's workstation is compromised, the attacker should not be able to "reach" the EMR core.
- Air-Gapped, Immutable Backups: We help you implement backup systems that are physically disconnected from the network and cannot be modified or deleted by an admin account.
- Endpoint Managed Detection (MDR): We provide 24/7 monitoring specifically tuned to identify the "encryption signatures" used by the Medusa syndicate, allowing us to kill the process before the first file is locked.
The Grivyonx View
At Grivyonx Cloud, we believe that Healthcare Security is a Human Right. We provide the expertise and the technical infrastructure to ensure that medical organizations can focus on saving lives, while we focus on saving their data. The nexus of state and crime is powerful, but our defense is stronger. Let's protect your mission together.
- #Lazarus Group
- #Medusa Ransomware
- #Cybersecurity
- #Healthcare Attacks
- #Ransomware
- #Threat Intelligence