Ransomware Freezes Japan Food Supply Chain
Introduction
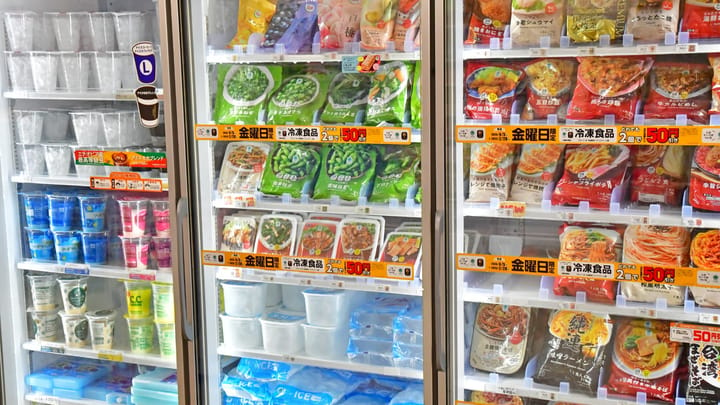
A significant cybersecurity incident has sent shockwaves through Japan's food service industry. Nichirei Logistics Group, a titan in the temperature-controlled logistics sector, confirmed a ransomware intrusion that has effectively paralyzed its warehouse management and distribution systems. The fallout is immediate and visible: thousands of restaurants, convenience stores, and institutional cafeterias have lost access to frozen inventory, with Kentucky Fried Chicken (KFC) Japan publicly acknowledging severe supply shortages across its vast network of outlets.
This event transcends a typical IT outage; it represents a direct strike on the physical supply chain. As the investigation unfolds, the incident underscores a growing reality for the logistics sector: digital resilience is now synonymous with operational survival. The attack highlights how threat actors are increasingly targeting the "nervous system" of commerce—logistics software—to maximize leverage and extortion potential.
The Anatomy of a Cold-Chain Crisis
The disruption began when unauthorized actors penetrated Nichirei's network, deploying encryption malware that locked down critical operational technology (OT) and enterprise resource planning (ERP) systems. Unlike standard data theft, this attack targeted the availability of systems that coordinate the movement of perishable goods—specifically the Warehouse Management Systems (WMS) that dictate inventory allocation, picking, and shipping schedules.
Because frozen logistics operate on razor-thin time margins—often measured in hours rather than days—any system downtime creates an immediate physical backlog. Trucks cannot be loaded without digital pick lists; inventory cannot be located without database queries; and temperature excursions risk total product loss if goods sit idle on docks. For KFC Japan, which relies heavily on a steady stream of frozen chicken and sides, the break in the chain meant menu items vanished from boards almost overnight.
Ripple Effects Across the Franchise Landscape
The impact radiates well beyond a single logistics provider or a single fast-food brand. Nichirei Logistics serves as a backbone for a massive ecosystem:
- Thousands of Endpoints: The company services approximately 5,000 to 6,000 client locations daily, ranging from major franchise chains to independent restaurants and school lunch programs.
- Just-in-Time Fragility: Modern food service operates on lean inventory models. Most outlets hold only 24 to 48 hours of frozen stock. A 72-hour system outage equates to empty freezers.
- Reputational Contagion: For brands like KFC, the inability to serve core menu items damages consumer trust and franchisee revenue simultaneously, creating a dual-front crisis management scenario.
Industry analysts suggest the total economic impact—spanning lost sales, spoilage costs, incident response fees, and potential regulatory fines—could climb into the tens of millions of dollars if remediation extends beyond the immediate week.
Why Logistics Is the New Frontline
Threat actors have pivoted strategically. Five years ago, ransomware gangs primarily targeted data-rich environments like healthcare or finance for double-extortion schemes (encrypt + threaten to leak). Today, the "availability" lever is proving far more profitable in sectors where downtime causes physical, irreversible consequences.
Logistics firms are uniquely vulnerable due to a convergence of factors: legacy OT systems (conveyors, automated storage/retrieval systems) often run on unpatchable operating systems; flat network architectures allow lateral movement from IT to OT easily; and the pressure to restore operations quickly makes victims more likely to pay ransoms. Nichirei's scale makes it a "big game hunting" trophy, but mid-sized cold-storage providers are equally at risk.
Grivyonx Expert Analysis
The Nichirei incident is a textbook case of "OT-IT convergence risk." Most logistics firms have digitized their warehouses—implementing WMS, TMS (Transport Management Systems), and IoT sensor networks—without segmenting these environments from corporate IT. When the initial access broker (likely via phishing or exploited VPN vulnerability) gained a foothold, they likely traversed a flat network straight into the warehouse control layer.
From a defensive posture, three controls would have materially altered this outcome: 1. Micro-segmentation enforcing zero-trust between the corporate LAN and the WMS/OT VLANs; 2. Immutable, Offline Backups of the WMS database and configuration files, tested quarterly for restore integrity; 3. OT-Specific Monitoring (anomaly detection on PLC/SCADA protocols) rather than relying solely on endpoint detection (EDR) which often lacks visibility into proprietary logistics protocols. Grivyonx Cloud's AI-driven segmentation engine is designed precisely to visualize and enforce these boundaries automatically, preventing lateral movement before it reaches the freezer aisle.
Regulatory and Compliance Aftershocks
Japan's revised Act on the Protection of Personal Information (APPI) and the Cybersecurity Basic Act impose strict notification timelines and security obligations on "Critical Information Infrastructure" operators. While food logistics has historically flown under the radar compared to finance or energy, this incident will likely accelerate regulatory designation of cold-chain logistics as critical infrastructure.
Expect the following shifts in the Japanese compliance landscape:
- Mandatory adoption of ISMS (Information Security Management Systems) certification for major 3PLs (Third-Party Logistics providers).
- Stricter supply chain risk management clauses in franchise agreements, forcing franchisors to audit the cyber hygiene of their logistics partners.
- Increased scrutiny from the Personal Information Protection Commission (PPC) regarding data breach notifications if customer or employee PII was exfiltrated during the encryption event.
Operational Resilience: The Path Forward
Recovery for Nichirei will not be a simple "decrypt and restart." Even with decryption keys (whether paid for or recovered), the integrity of the WMS data must be validated. Corrupted inventory records—showing stock that doesn't exist or missing stock that does—could cause weeks of manual reconciliation. The industry must treat this as a watershed moment for "Cyber-Physical Resilience."
Key strategic imperatives for logistics operators globally now include:
- Tabletop Exercises: Quarterly simulations involving IT, OT, warehouse floor managers, and key clients (like franchise operations teams) to practice manual fallback procedures.
- Decoupled Operations: Maintaining the capability to run "paper-based" or "offline mode" picking for 72 hours using printed manifests and radio communication.
- Vendor Risk Tiering: Classifying logistics providers as Tier-1 critical vendors requiring continuous threat exposure management, not just annual questionnaires.
Conclusion
The ransomware attack on Nichirei Logistics is more than a headline; it is a stress test the industry failed. It proves that the freezer aisle is now a frontier in cyber warfare. As supply chains digitize further—embracing AI-driven demand forecasting, autonomous forklifts, and blockchain traceability—the attack surface expands exponentially. Organizations that view cybersecurity as a back-office cost center rather than a core operational competency will find their goods thawing on the loading dock.
Building resilience requires more than patching servers; it demands architectural segregation, immutable recovery architectures, and AI-powered visibility into the convergence of IT and OT. At Grivyonx Cloud, we specialize in securing this exact intersection, ensuring that the digital backbone of your physical operations remains unbreakable, so your supply chain never goes cold.
- #ransomware
- #cybersecurity
- #supply chain
- #japan
- #nichirei logistics
- #kfc
- #critical infrastructure
- #incident response