Yubico Launches YubiID and Post‑Quantum YubiKey Beta
Introduction
Yubico has announced two complementary moves that aim to tighten the chain between a user’s proven identity and the cryptographic credentials they use every day. The first is YubiID, a cloud‑delivered service that binds identity verification directly to credential enrollment and recovery across existing identity platforms. The second is a beta‑program for a post‑quantum‑ready YubiKey, signaling the vendor’s preparation for the next generation of cryptographic threats. Together, these releases address a long‑standing blind spot: even when authentication is phishing‑resistant, the process that establishes and restores a user’s trusted identity can remain vulnerable.
The Identity Verification Gap
Modern phishing‑resistant authenticators such as FIDO2 tokens excel at proving possession of a private key during a login ceremony. However, the initial registration of that key—and the subsequent recovery when a token is lost—often relies on weaker factors like email links, SMS codes, or knowledge‑based questions. Attackers who compromise those auxiliary channels can inject a malicious credential into a victim’s account, bypassing the strong authenticator entirely. Yubico’s analysis highlights that closing this gap requires a unified workflow where identity proofing, credential issuance, and recovery are cryptographically linked from start to finish.
YubiID Service Overview
YubiID is positioned as an identity‑verification layer that sits between an organization’s identity provider (IdP) and the hardware authenticator fleet. When a new employee or partner is onboarded, YubiID orchestrates a verified identity check—leveraging the IdP’s existing assurance levels—and then automatically provisions a FIDO2 credential onto a YubiKey. If the token is later lost, the same verified identity context drives a secure, auditable re‑enrollment without falling back to insecure reset paths. The service integrates through standard protocols such as SCIM and OpenID Connect, allowing it to slot into current IAM stacks without custom development.
Post‑Quantum YubiKey Beta
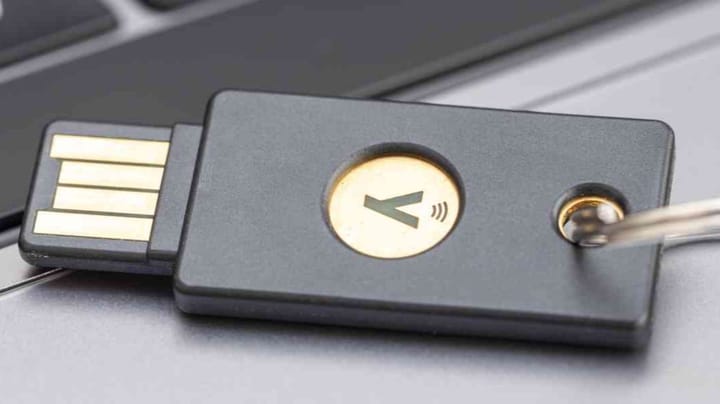
In parallel, Yubico has opened a beta for a YubiKey model that incorporates lattice‑based cryptographic algorithms approved by the NIST post‑quantum standardization process. The device retains the familiar form factor and USB/NFC interfaces while adding a firmware path that can negotiate quantum‑resistant key exchange and signatures. Early adopters can test interoperability with libraries that support the new algorithms, giving security teams a head start on migration before quantum‑capable adversaries become a realistic threat.
Practical Steps for Defenders
- Map the enrollment lifecycle: Document every step from identity proofing to credential issuance and recovery. Identify any stage that relies on non‑phishing‑resistant factors.
- Adopt a unified verification service: Evaluate YubiID or equivalent solutions that cryptographically bind identity assurance to credential provisioning, eliminating fallback to weak reset mechanisms.
- Pilot post‑quantum hardware: Enroll a subset of high‑value users in the YubiKey beta to validate firmware stability, application compatibility, and operational processes for key rotation.
- Update policy and training: Revise authentication policies to require verified identity for any credential enrollment or recovery action. Train help‑desk staff on the new workflow to prevent social‑engineering shortcuts.
- Monitor for anomalies: Deploy logging and alerting on enrollment and recovery events, correlating them with identity‑verification outcomes to detect unauthorized credential injection.
Grivyonx Expert Analysis
Yubico’s dual announcement underscores a maturation of the authentication market: vendors are no longer treating strong authenticators as isolated tokens but as components of an end‑to‑end identity fabric. By embedding verification into the enrollment pipeline, YubiID removes the most common attack surface—account recovery—while the post‑quantum YubiKey beta gives forward‑looking organizations a concrete migration path. Security teams should treat these moves as a catalyst to audit their own identity‑proofing processes and to begin budgeting for quantum‑ready hardware refresh cycles.
Conclusion
The combination of a verification‑centric enrollment service and a quantum‑resistant authenticator signals a shift toward holistic identity security that addresses both today’s phishing tactics and tomorrow’s cryptographic breakthroughs. Organizations that integrate these capabilities into their IAM strategy will reduce the attack surface around credential lifecycle management and position themselves for a smoother transition to post‑quantum cryptography. Grivyonx’s AI‑driven DevSecOps automation can help teams continuously validate these controls across cloud and on‑premise environments.
- #Yubico
- #YubiID
- #YubiKey
- #post-quantum
- #phishing-resistant
- #identity verification
- #authentication



