ServicesBlogPricingContactContact Now

Grivyonx Intelligence Hub

Intelligence Hub Archive - Page 36

Older cybersecurity, AI and cloud security analysis from the Grivyonx research team.

Cyber Security

Global Cyber Fraud Crackdown: INTERPOL's Jackal IV Operation

In a sweeping eight-month operation, INTERPOL arrested 58 individuals and flagged 263 suspects linked to West African organized crime networks behind global cyber fraud. The effort, known as Operation Jackal IV, united 22 countries across six continents to dismantle the financial and digital operations of groups like Black Axe. Law enforcement agencies seized millions in illicit funds, froze suspicious bank accounts, and intercepted fraudulent online activities that span romance scams, business email compromise schemes, and large-scale money laundering operations across the world.

By Gourav Rajput

Cyber Security

SLEEPWALKER Backdoor: Silent Until One Packet Triggers

Independent researcher uncovered a previously unknown Windows backdoor named SLEEPWALKER that remains dormant until a crafted network packet triggers its custom 23‑instruction bytecode. The unsigned 64‑bit DLL stays inert in memory, showing no activity until the precise packet arrives, at which point it awakens and executes its own command language.

By Gourav Rajput

Cloud

Critical Gitea RCE Flaw Exploited in the Wild

A severe remote code execution vulnerability in Gitea is now being actively exploited, prompting an urgent warning from CISA. The flaw, tracked as CVE-2026-60004, carries the maximum severity rating and has been linked to attacks dropping cryptocurrency-mining malware. Organizations running self-hosted Gitea instances are urged to patch immediately to prevent full system compromise.

By Gourav Rajput

AI

AI-Powered Apple Support Scams Target Stolen Device Owners

Cybersecurity researchers have uncovered a highly organized phishing operation that weaponizes artificial intelligence to target individuals whose Apple devices have been stolen. The service automates social engineering attacks using convincing AI-generated voice calls.

By Gourav Rajput

AI

How AI Coding Tools Empower Non-Developers to Build Software Faster

The modern business landscape demands agility, and companies that can rapidly translate ideas into functional products hold a significant competitive edge. However, traditional software development has always been bottlenecked by limited technical resources.

By Gourav Rajput

AI

Hugging Face Security Breach: OpenAI's Response & Future of AI Safety

A recent security incident involving Hugging Face and OpenAI has sparked important conversations about AI model safety. OpenAI has shared detailed findings about what happened, revealing vulnerabilities in third-party platforms and the urgent need for stronger security measures across the AI ecosystem. The incident highlights growing concerns about how artificial intelligence models are shared, stored, and protected from malicious actors seeking to exploit these powerful systems.

By Gourav Rajput

AI

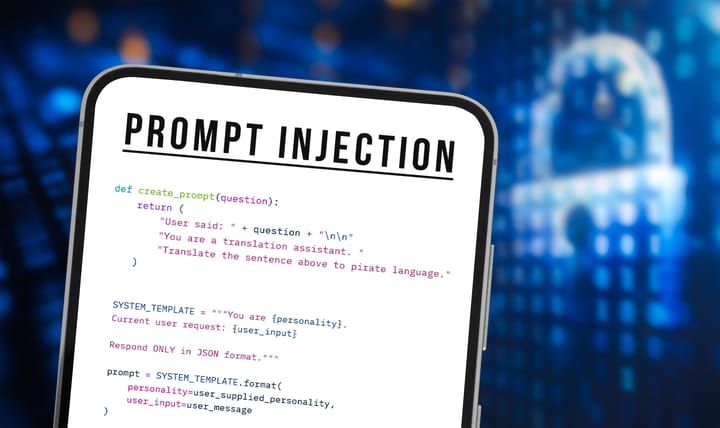
Invisible HTML Tricks AI Email Summaries Into Lies

A novel attack vector is targeting AI-powered email assistants by embedding invisible HTML instructions within messages. These hidden prompts manipulate summarization engines into generating false, malicious, or dangerous outputs without the user's knowledge. As organizations increasingly rely on large language models to manage communication, understanding this 'prompt injection' technique is critical for maintaining data integrity and operational security.

By Gourav Rajput

AI

OpenClaw Vulnerability Exposes AI Models to Poisoning

A recently disclosed security weakness in NVIDIA's OpenClaw tool has raised alarms across the AI community. Researchers found that the networking flaw allows malicious actors to access local model servers without authentication, opening the door to a dangerous type of attack known as LLM poisoning. By exploiting the Ollama API, adversaries can inject corrupted data into large language models, potentially leading to persistent manipulation of AI agent behavior. The findings highlight the growing intersection between networking vulnerabilities and artificial intelligence security.

By Gourav Rajput

Cyber Security

US Slaps Sanctions on Iranian Hackers Over Infrastructure Attacks

The U.S. government has intensified its crackdown on Iranian cyber operations by imposing new sanctions against operatives linked to Tehran's state-sponsored hacking programs. The action represents a significant escalation in Washington's ongoing efforts to disrupt malicious cyber activities targeting American assets and infrastructure.

By Gourav Rajput

Cloud

Cyber Security Costs Surge, Leaving Small Firms Vulnerable

As digital threats become more costly, the financial burden on organizations is escalating dramatically. Record‑breaking breach expenses and soaring defense budgets are reshaping the security landscape, leaving many small enterprises especially exposed. The ripple effect threatens entire supply chains, amplifying the urgency for affordable protection.

By Gourav Rajput

AI

Critical NVIDIA NemoClaw Flaw Exposes Local AI Models to Web Attacks

Security researchers have identified a significant vulnerability in NVIDIA's NemoClaw framework that could allow malicious actors to compromise local AI installations through nothing more than a carefully crafted webpage. The flaw, discovered by Oasis Security, exposes AI agents running on Ollama to unauthorized access and potential model manipulation.

By Gourav Rajput

Cyber Security

WhatsApp Passkey Update Strengthens Cross-Platform Login Security

Meta has rolled out a significant security enhancement for WhatsApp, allowing users to register multiple passkeys on a single account. The update works seamlessly across both iOS and Android devices, giving over a billion people a simpler and safer way to log in. By moving away from traditional SMS-based verification, WhatsApp is taking a strong step toward reducing phishing risks and improving user experience across the platform.

By Gourav Rajput

Cloud

Mirage2FA Phishing Campaign Compromises 4500 US and EU Firms

A sophisticated phishing-as-a-service toolkit known as Mirage2FA has emerged as a significant threat to enterprise cybersecurity, successfully compromising thousands of Microsoft 365 accounts across the United States and European Union. The campaign leverages legitimate authentication mechanisms to bypass two-factor authentication protections, leaving organizations vulnerable to data breaches and unauthorized access.

By Gourav Rajput

Cyber Security

Malicious npm Packages Exploit unpkg to Spread Phishing Pages

Cybersecurity researchers have uncovered a sophisticated phishing operation involving 24 malicious npm packages. Instead of installing harmful code on developer machines, threat actors are leveraging these packages as free web hosting infrastructure. By using the unpkg content delivery network, attackers are serving convincing fake Cloudflare CAPTCHA pages designed to redirect users to credential-stealing sites. This creative abuse of legitimate developer tools highlights the evolving tactics used in modern social engineering attacks.

By Gourav Rajput

Cyber Security

E4del and PINHOLE RATs Hide C2 Commands in FTP Banners

A newly uncovered cyber campaign is weaponizing ordinary FTP server banners, turning them into covert channels that deliver commands to two stealthy remote access trojans known as E4del and PINHOLE. By embedding C2 instructions in plain sight, the operators are exploiting a technique called dead drop resolving to stay hidden in everyday network traffic. This approach marks a sharp escalation in attacker tradecraft. Instead of relying on suspicious domains or hardcoded IP addresses, the malware quietly reads instructions from infrastructure that most security teams would never think to flag. The result is a highly evasive operation that challenges traditional threat detection and demands a rethink of how organizations monitor seemingly benign network services.

By Gourav Rajput

AI

How Frontier AI Revolutionizes Vulnerability Management

Vulnerability management has long been defined by an endless cycle of scan, prioritize, and patch—a process strained by expanding attack surfaces and talent shortages. Frontier AI is fundamentally rewriting this paradigm, shifting organizations from reactive remediation to predictive, risk-based defense. By fusing massive threat intelligence datasets with contextual business logic, AI-driven platforms now predict which flaws will be exploited before attackers act, automate validation at scale, and orchestrate remediation across hybrid environments without human bottlenecks.

By Gourav Rajput

AI

How AI's Full Tech Stack Powers Intelligence at Scale

The artificial intelligence revolution isn't powered by a single breakthrough—it's the result of simultaneous advances across multiple layers of technology. OpenAI CFO Sarah Friar recently outlined how the compounding effect of improvements in hardware, infrastructure, and software is making AI more capable and affordable than ever before.

By Gourav Rajput